Security at Querri: Built on Trust, Designed for Protection
We safeguard your data with transparent, enterprise-grade security practices. Focus on insights without worrying about data loss, breaches, or misuse.
Compliance & Security
Our security practices allow you to focus on insights without worrying about data loss, breaches, or misuse.


Independently Verified
Annual compliance audits ensure
your data stays protected
How we protect your information
Your data is yours - we never use your data to train AI
Your data stays private. No information is shared between customers. Everything remains isolated, keeping your business confidential.
Encryption & Key Management
We protect customer data with AES-256 encryption at rest and TLS in transit. Keys are managed in AWS KMS with strict access controls, so decryption keys are never tied to user accounts. Every customer organization also gets its own database and its own storage bucket.
Granular Access Control
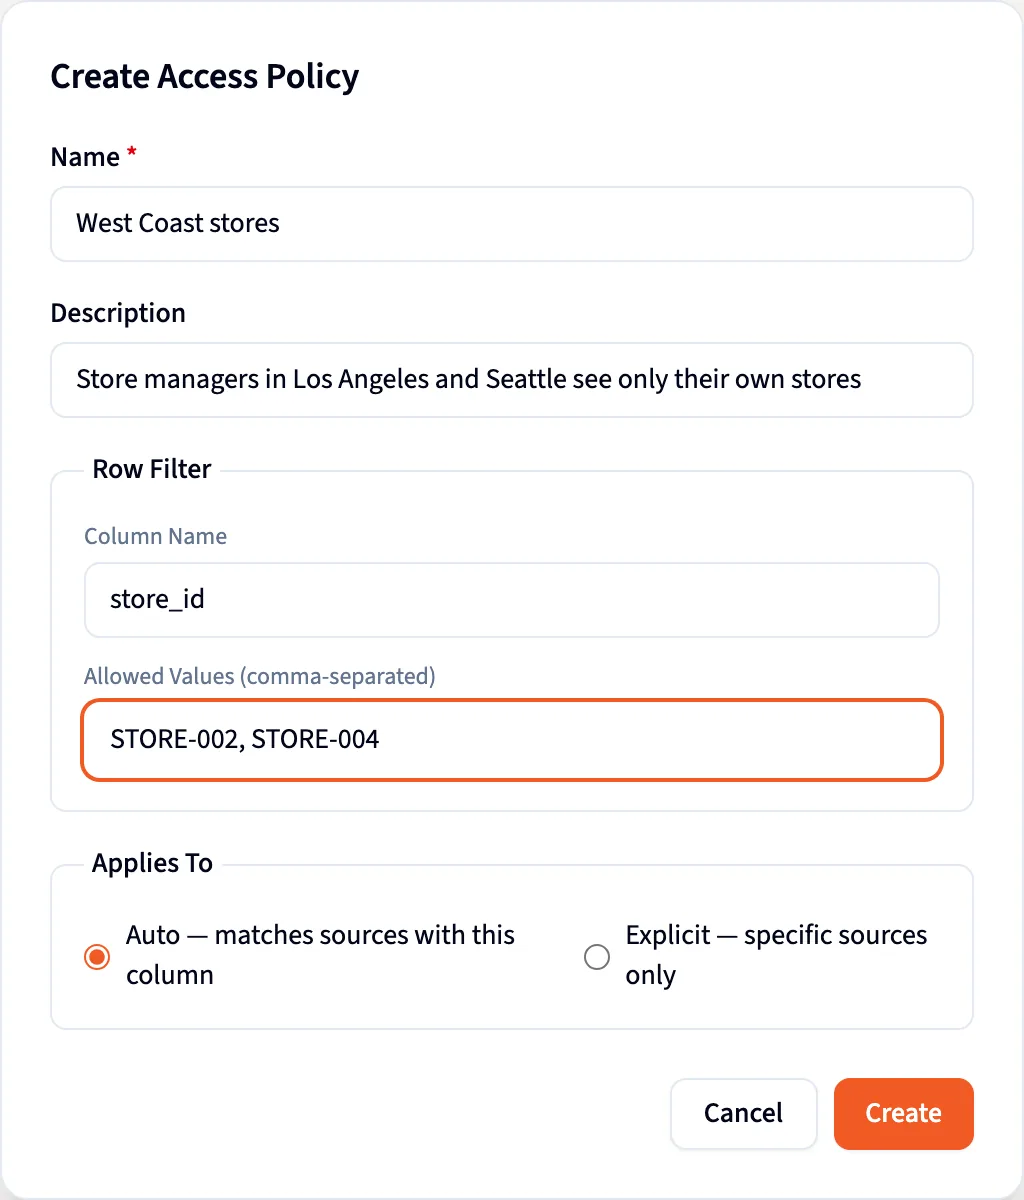
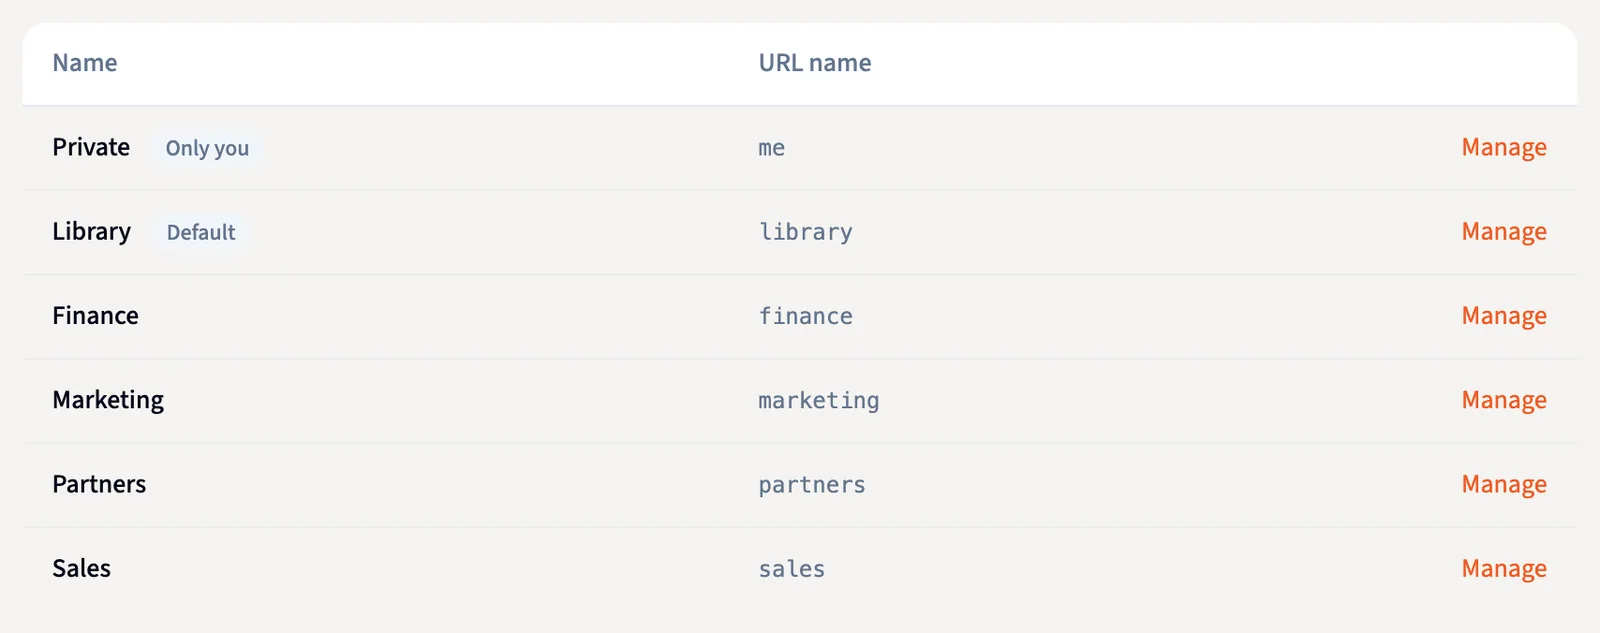
Access is granted based on the principle of least privilege through role-based access control (RBAC). Single sign-on (SSO), just-in-time credentials, and multi-factor authentication are integrated to ensure only the right people can access the right resources at the right time. Querri's layered sharing model lets you control who sees your data, which rows they see, and how access is governed across teams — from private-by-default projects all the way to workspace-level boundaries. Learn more in our docs →
Isolation & Data Privacy
Our infrastructure is designed around isolated tenants, ensuring each project is its own secure boundary. By default, no access is allowed unless explicitly authorized, preventing data from crossing between tenants or accounts.
Encryption in Transit & at Rest
We adopt industry-standard cryptography, enforcing TLS for all data in motion and AES-256 encryption for data at rest. Load balancers automatically enforce HTTPS with the latest cipher suites, ensuring data confidentiality during transfer.
Compliance & Certifications
Querri is SOC 2 Type II, HIPAA and ISO 27001:2022 certified — each independently verified. These certifications confirm that our security controls are not just designed well, but operating effectively, and we continuously update our practices to meet evolving compliance requirements.
Audit Logging & Monitoring
Every access and system change is tracked across multiple layers, including AWS CloudTrail, ELK logging, and Wazuh agents. Logs are tamper-resistant, centralized, and continuously monitored to detect anomalies or unauthorized behavior.
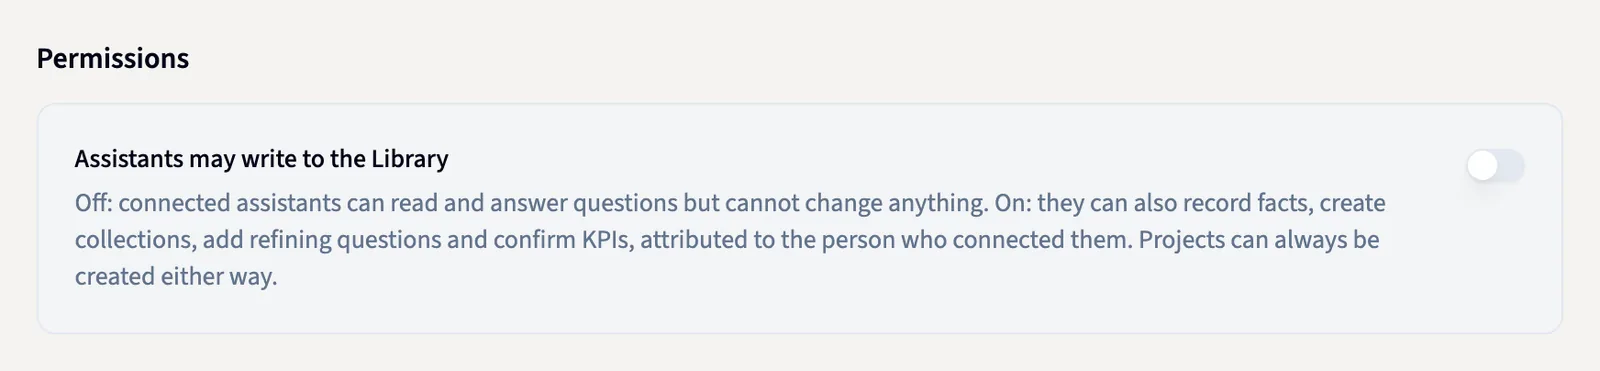
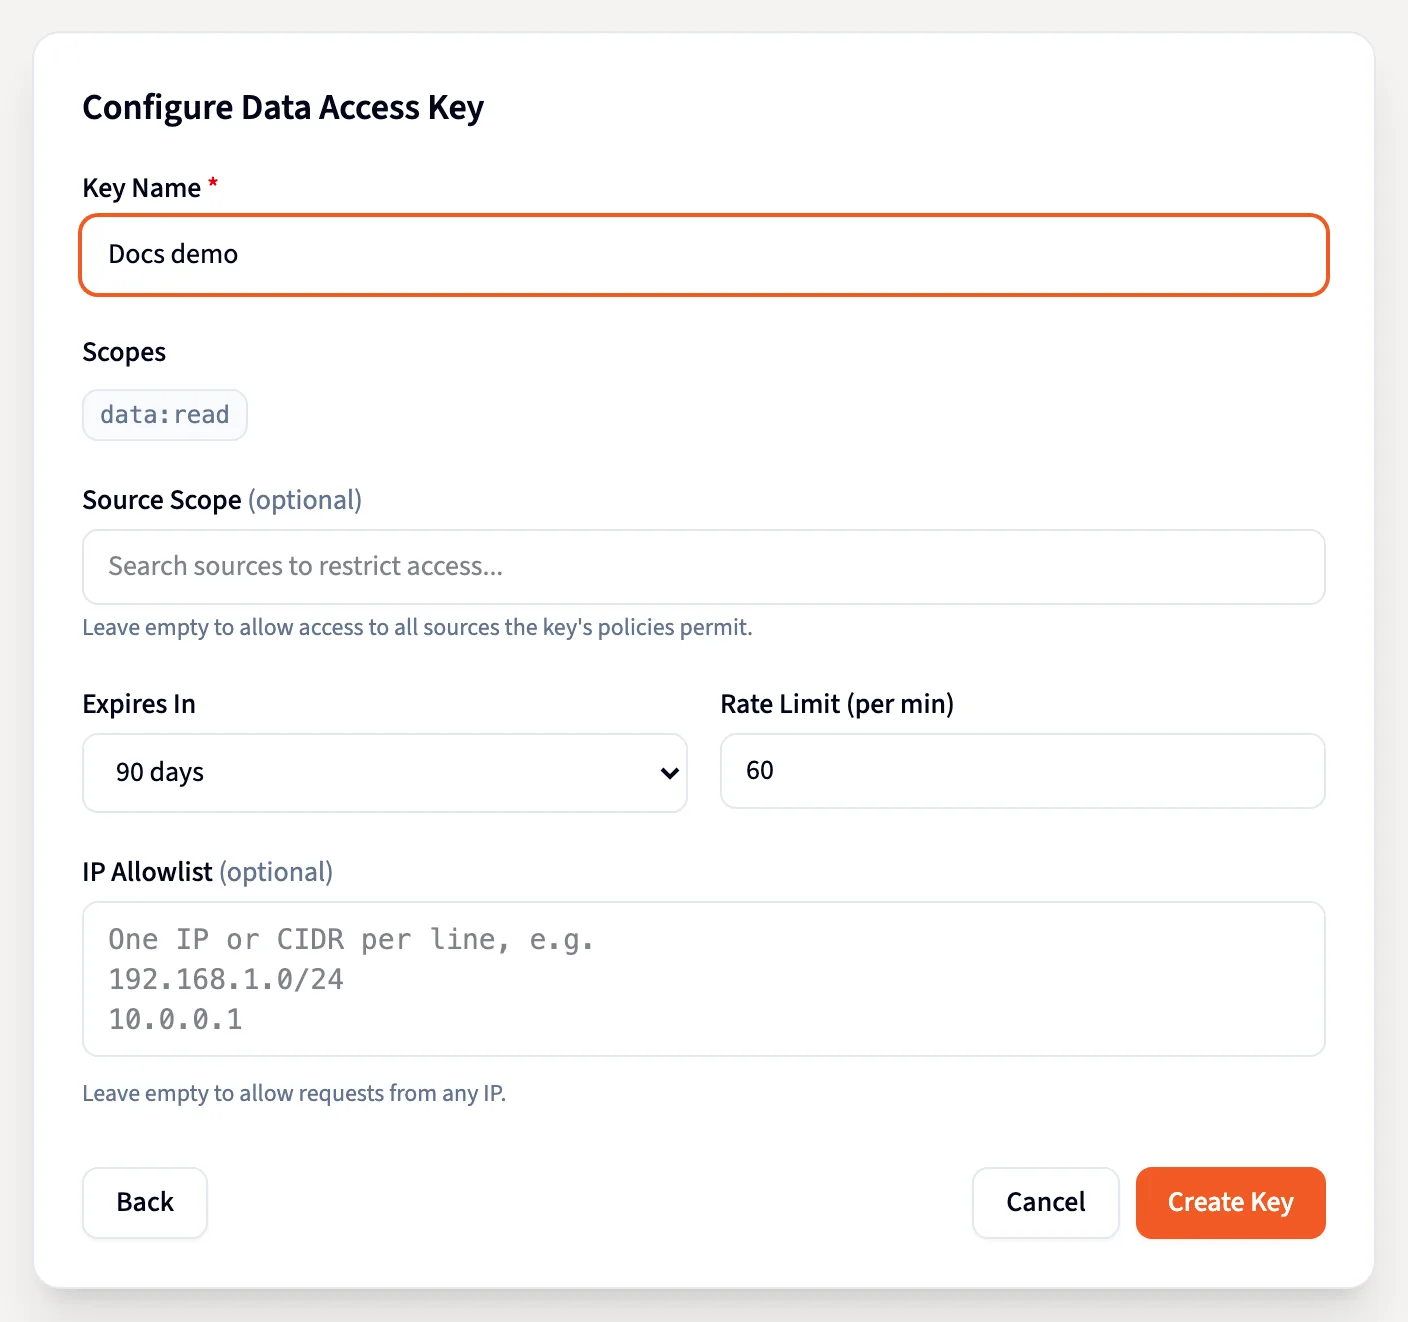
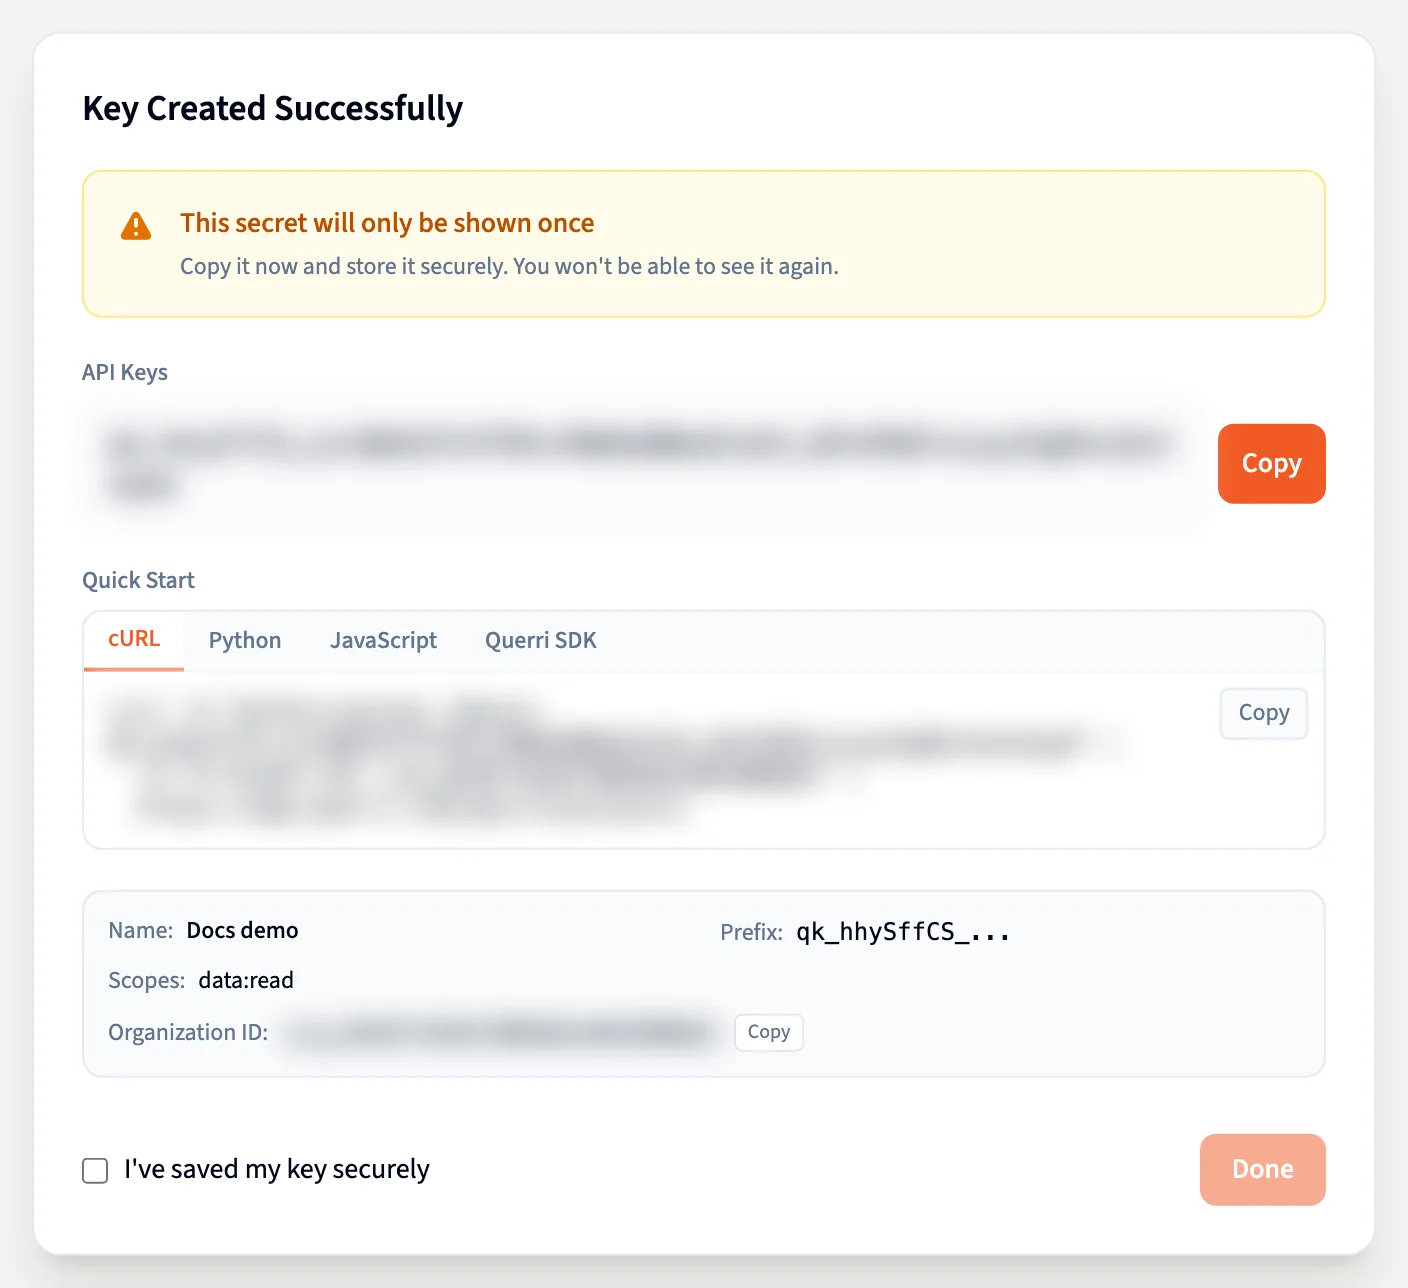
In the app
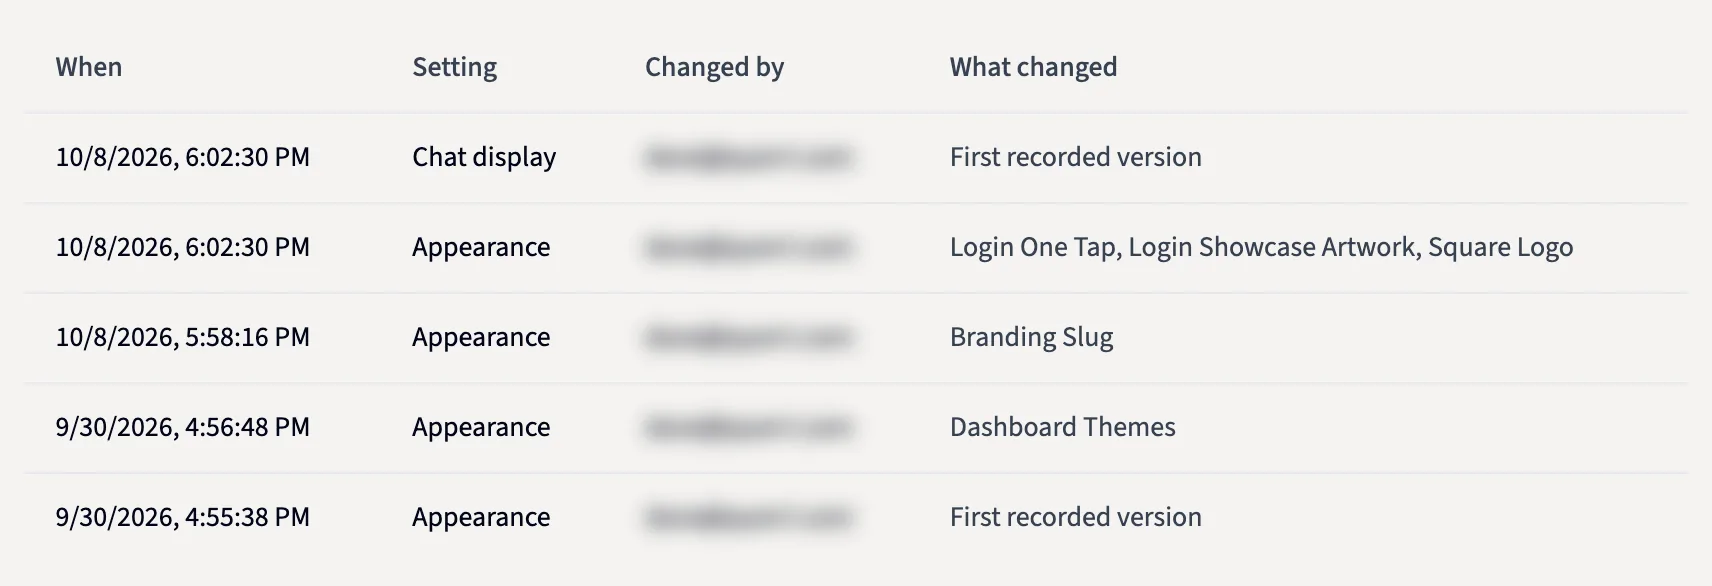
The controls your admins set
These are screenshots of Querri with a demo company's data.
"Security has been at the heartDave Ingram, Querri Founder/CEO
of Querri from the first line
of code I wrote."
More Questions? Check out our FAQs
Querri secures data with layered protections, including encryption at rest and in transit, isolated tenant environments, strict role-based access controls, continuous monitoring, and independently audited compliance certifications.
Yes. All data is encrypted with AES-256 at rest and TLS in transit. Encryption keys are managed in AWS KMS, isolated and never tied to user accounts, and every customer organization gets its own database and storage.
Access is tightly controlled using role-based access control (RBAC), single sign-on (SSO), and just-in-time tokens that expire quickly. Multi-factor authentication is enforced, and all access attempts are logged and monitored.
No. Your data is isolated to your tenant environment and never used to train Querri's AI models or shared across accounts.
We employ 24/7 monitoring with AWS GuardDuty, Wazuh SIEM, and AWS Inspector to detect anomalies, intrusions, or vulnerabilities. Alerts trigger formal incident response procedures to quickly investigate and remediate issues.
Querri is SOC 2 Type II, HIPAA and ISO 27001:2022 certified, all independently verified, and we continuously update our controls to meet evolving requirements.
Querri has formal incident response procedures in place. We rapidly detect, report, and mitigate incidents, while documenting outcomes and ensuring continuity of service.
Our platform is deployed across multiple availability zones with automated failover, backups, and disaster recovery procedures to ensure reliability and minimize downtime.
We continuously scan for vulnerabilities using AWS Inspector and Wazuh, patching critical issues quickly. File integrity monitoring and antivirus scanning provide additional protection against malware or unauthorized changes.
If you believe you've found a security issue in Querri, please report it privately to security@querri.com. We follow responsible disclosure practices and work with good-faith researchers to investigate and fix issues before public disclosure.
Yes. We share our SOC 2 Type II, HIPAA, and ISO 27001:2022 compliance reports under NDA with customers, partners, or prospects who request them by contacting security@querri.com.